Inventory everything
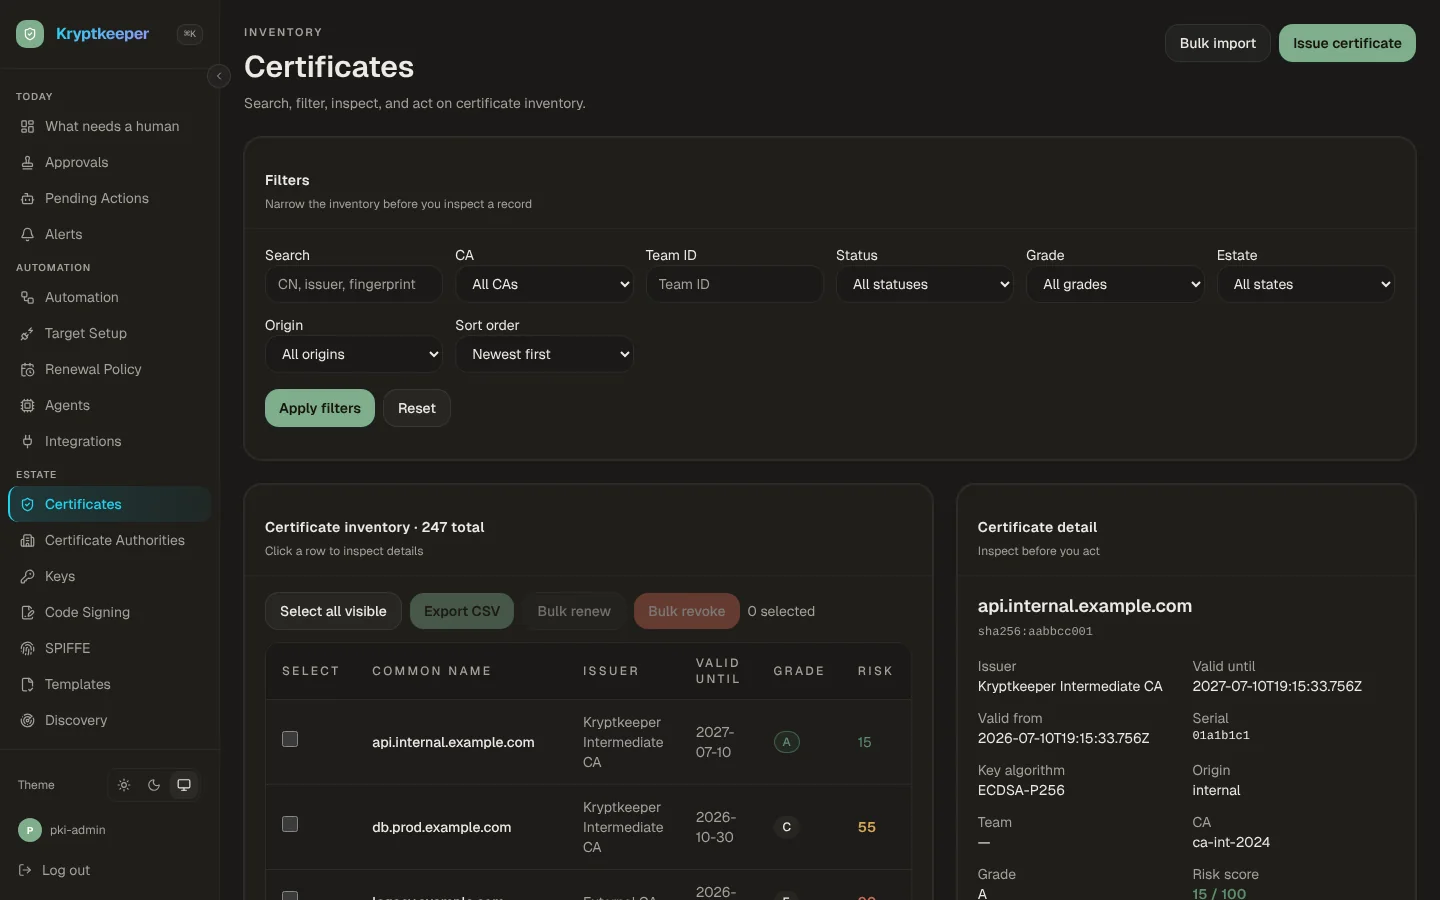
Network discovery scanning, agentless SSH and WinRM, CT-log monitoring, bulk import of PEM, PKCS#7 and CSV, and sync from ADCS.
KryptKeeper is an open-source PKI and certificate lifecycle platform. It runs your certificate authorities, finds every certificate in your estate, including ones it never issued, and shows a person exactly what needs them today.
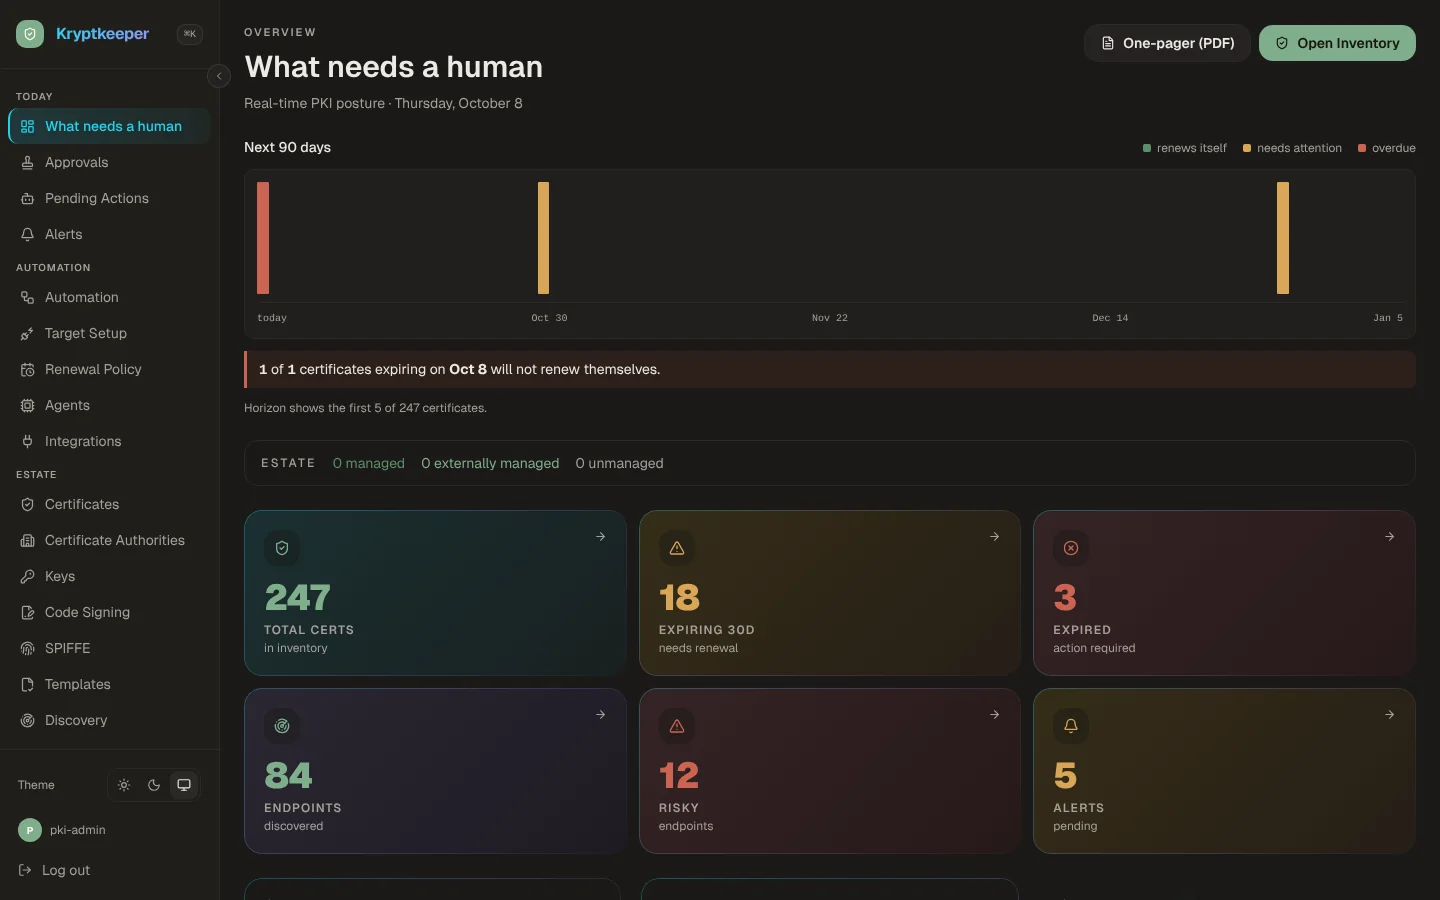
Most organizations hold certificates from DigiCert, Sectigo, Let's Encrypt, Active Directory Certificate Services and a few forgotten issuers from old acquisitions. Nobody has the full list, so the first sign of trouble is an outage when one expires.
KryptKeeper starts with visibility. Every certificate it knows about gets an origin (issued here, imported, discovered or synced) and a management state: managed, external, or unmanaged, which is the risk column. From any unmanaged row, one flow assigns an owner and a path to manage it.
Network discovery scanning, agentless SSH and WinRM, CT-log monitoring, bulk import of PEM, PKCS#7 and CSV, and sync from ADCS.
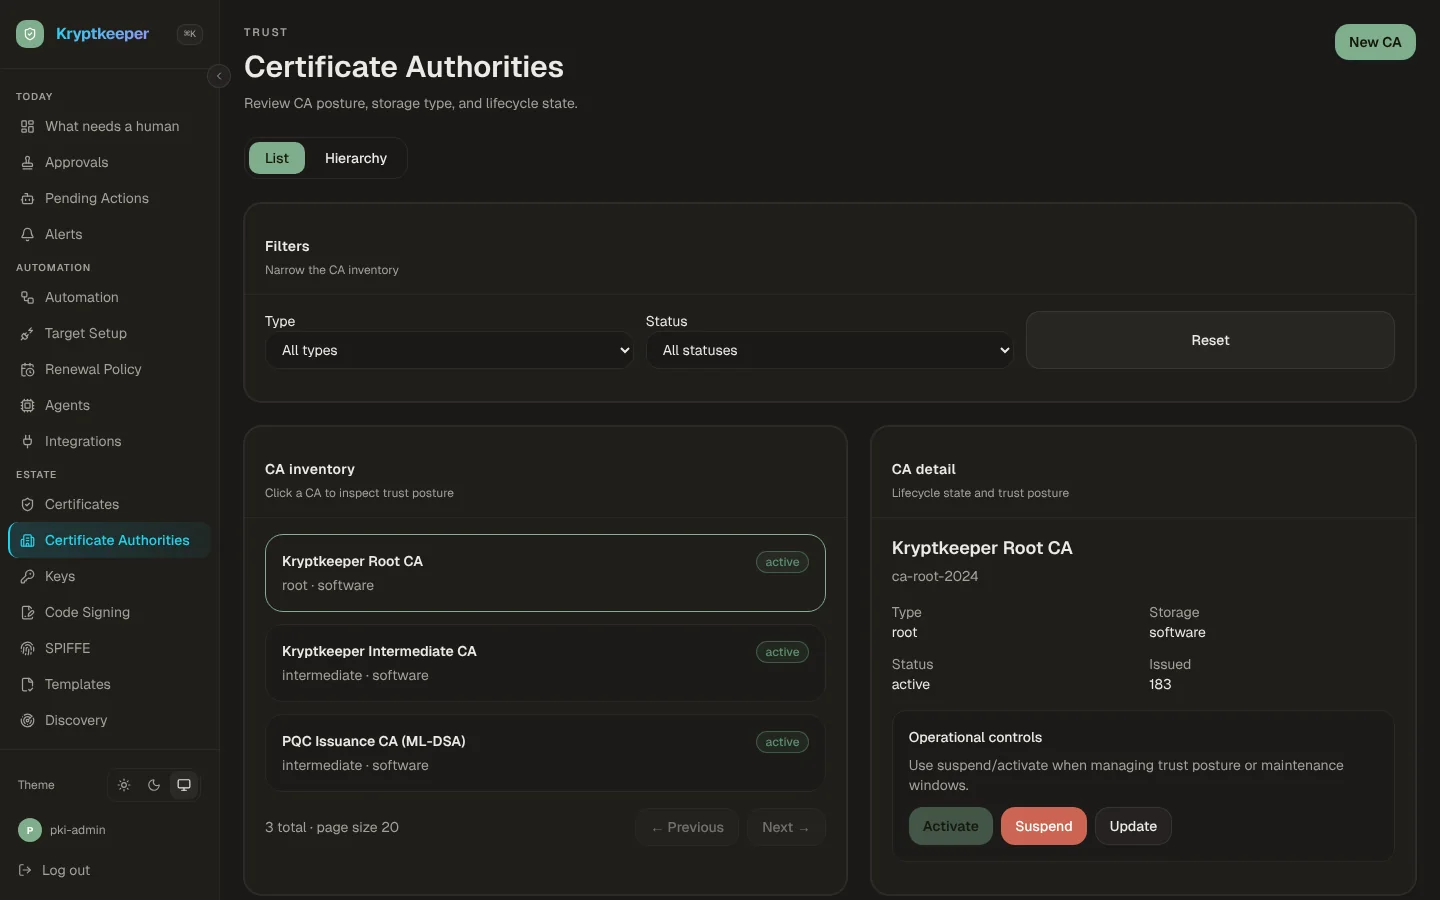
Root and issuing CAs, templates, approvals, renewal autopilot, bulk revoke and re-issue, and key rotation with passphrase-wrapped backups.
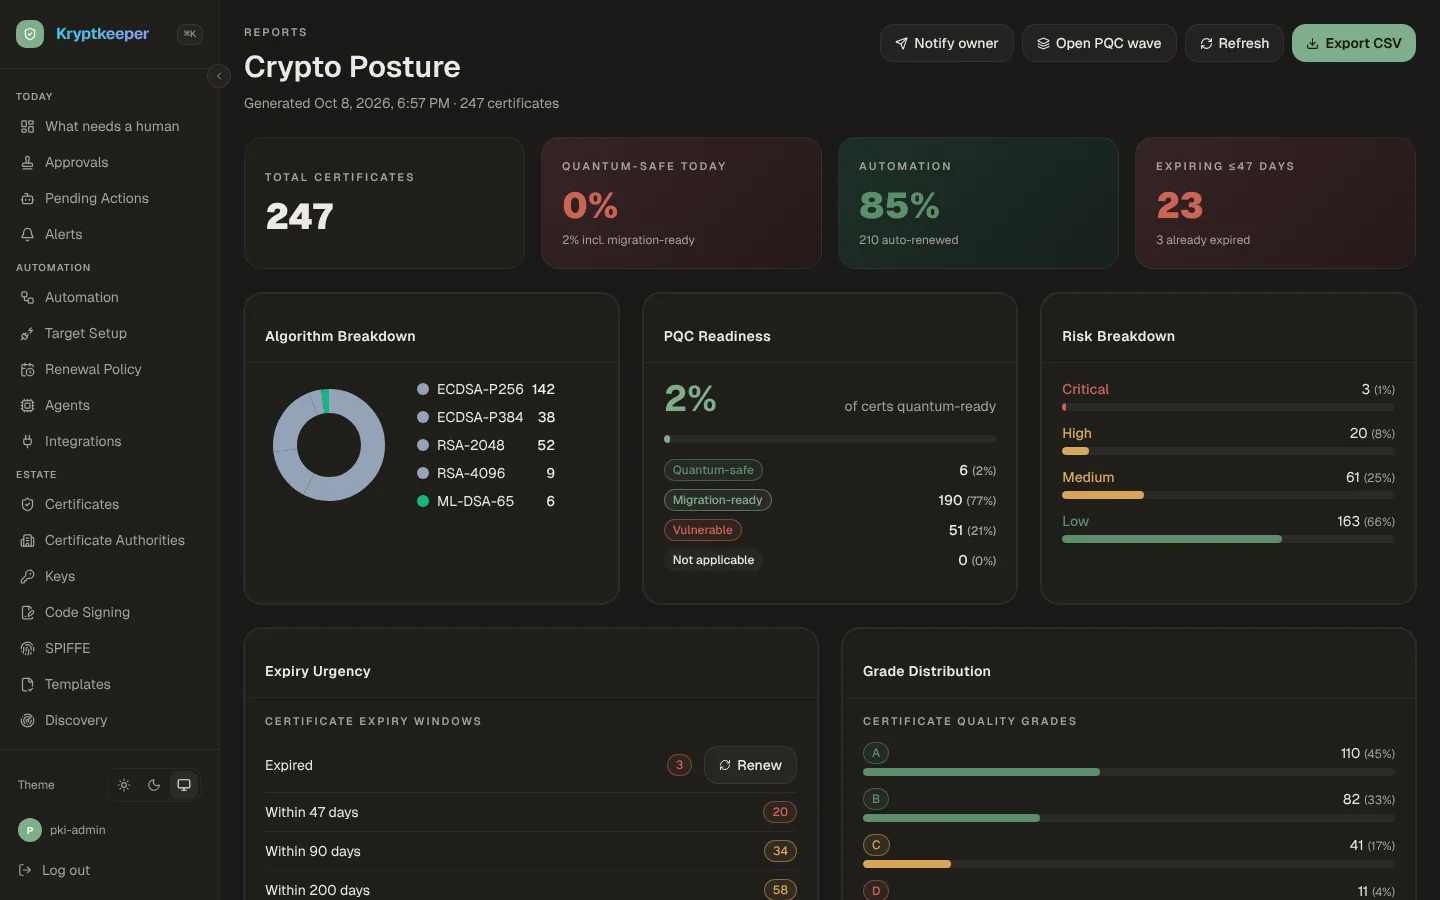
An append-only audit log, SOC 2 and PCI DSS evidence packs, CA health, expiry timelines and an algorithm-sunset report for post-2030 compliance.
The CA engine, the API and every protocol endpoint run in one binary. The dashboard is a compiled React app. Signing always goes through Go's crypto.Signer, so swapping key storage never touches CA logic.
| Protocol | RFC | Used for |
|---|---|---|
| ACME | 8555 | Web server TLS with certbot or acme.sh |
| EST | 7030 | Enterprise device enrollment |
| SCEP | n/a | Network devices: F5, Citrix, Palo Alto |
| OCSP | 5019 | Real-time revocation checks |
| CRL | 5280 | Revocation lists |
| CMP | 4210 | Certificate Management Protocol |
| MS-XCEP / MS-WSTEP | n/a | Windows auto-enrollment, replacing ADCS |
Docker Compose for a single node, a Helm chart for Kubernetes, or the plain binary. TLS on by default, and it refuses to start on missing secrets.
Apache 2.0. The core CA, every protocol server, discovery and the dashboard stay free.